Reusable KYC
Reusable KYC
Reusable KYC powered by live fraud intelligence
Move verified users into new products and partner flows without repeating KYC. Sardine captures consent and checks the live session for risk before anything is reused.
Don’t make good users repeatedly prove themselves
Expand customer access across partners and products without relaxing risk controls
Partner Onboarding
Reduce friction when bringing new partners into your ecosystem
Expand your partner network with fewer operational and contractual hurdles, while giving each partner a way to participate in consent-based identity sharing.
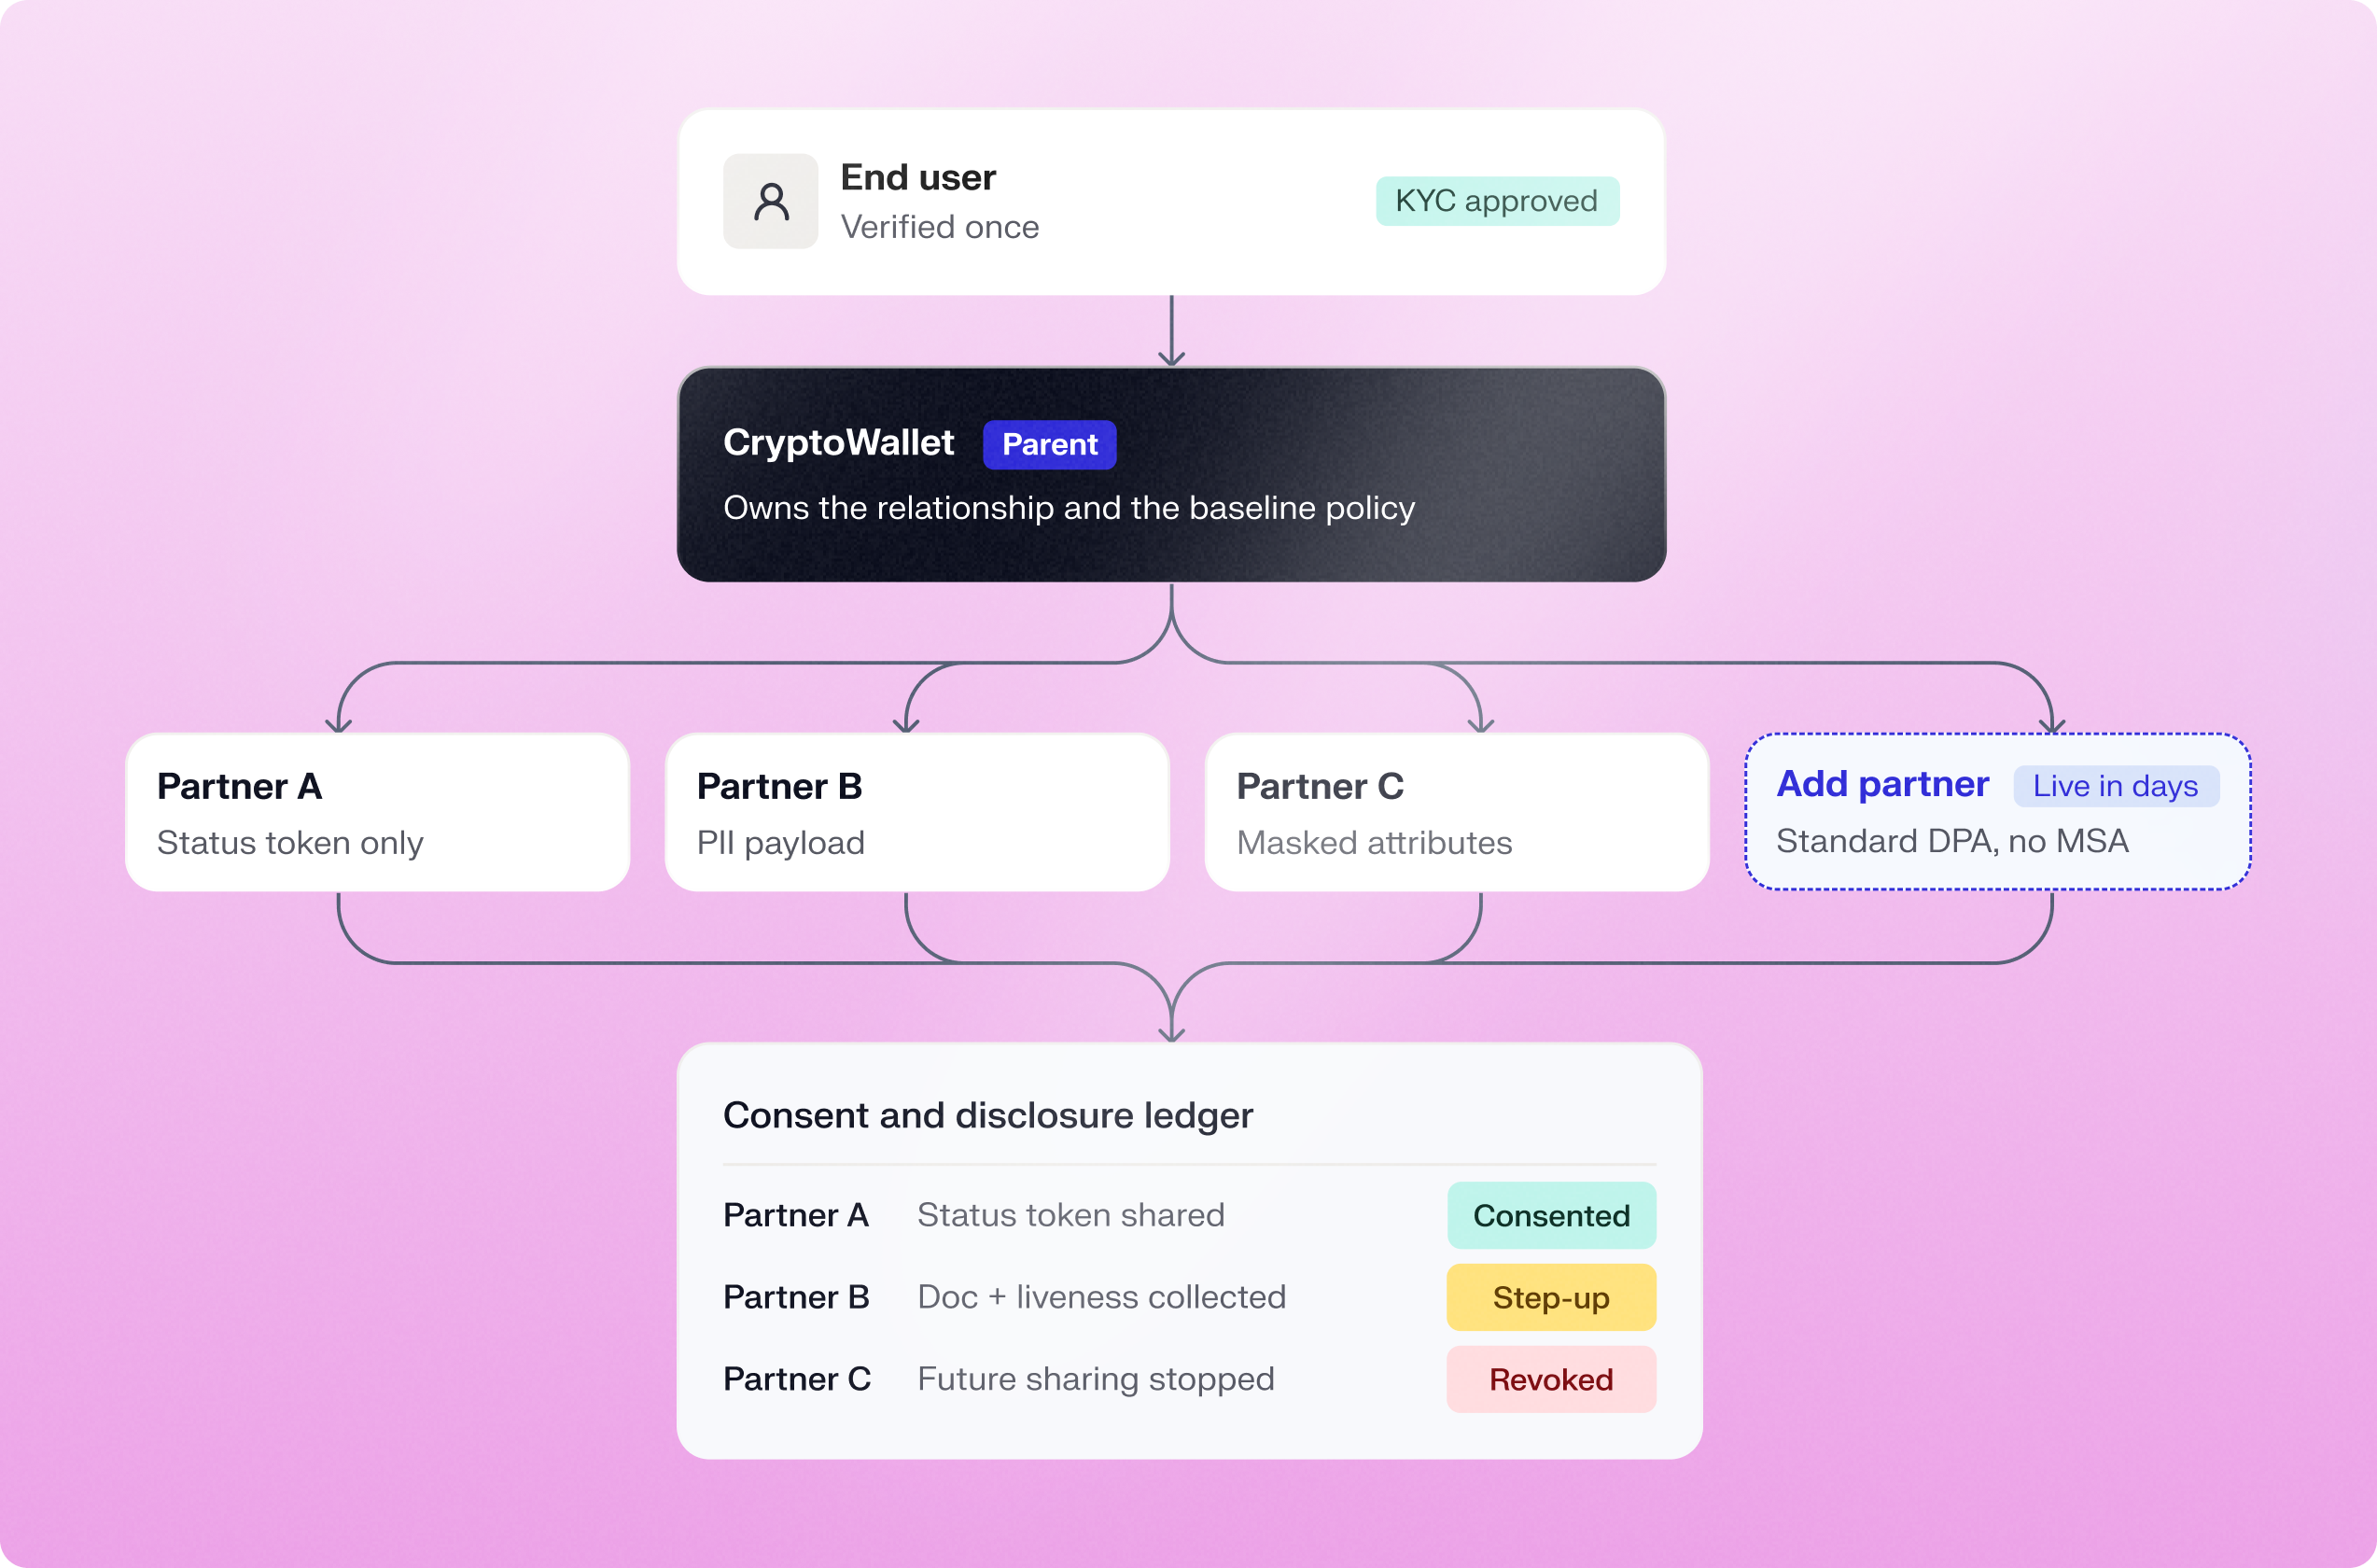

Use Sardine’s platform or integrate directly via API to fit your existing workflows.

Use a standard DPA without negotiating a full MSA for every relationship.

Support customer journeys with embedded and redirect-based flows.
Customer Growth
Acquire and retain more customers by reusing verified identities
Turn your network of verified users into an acquisition channel while removing friction that can prevent customers from completing onboarding or returning.
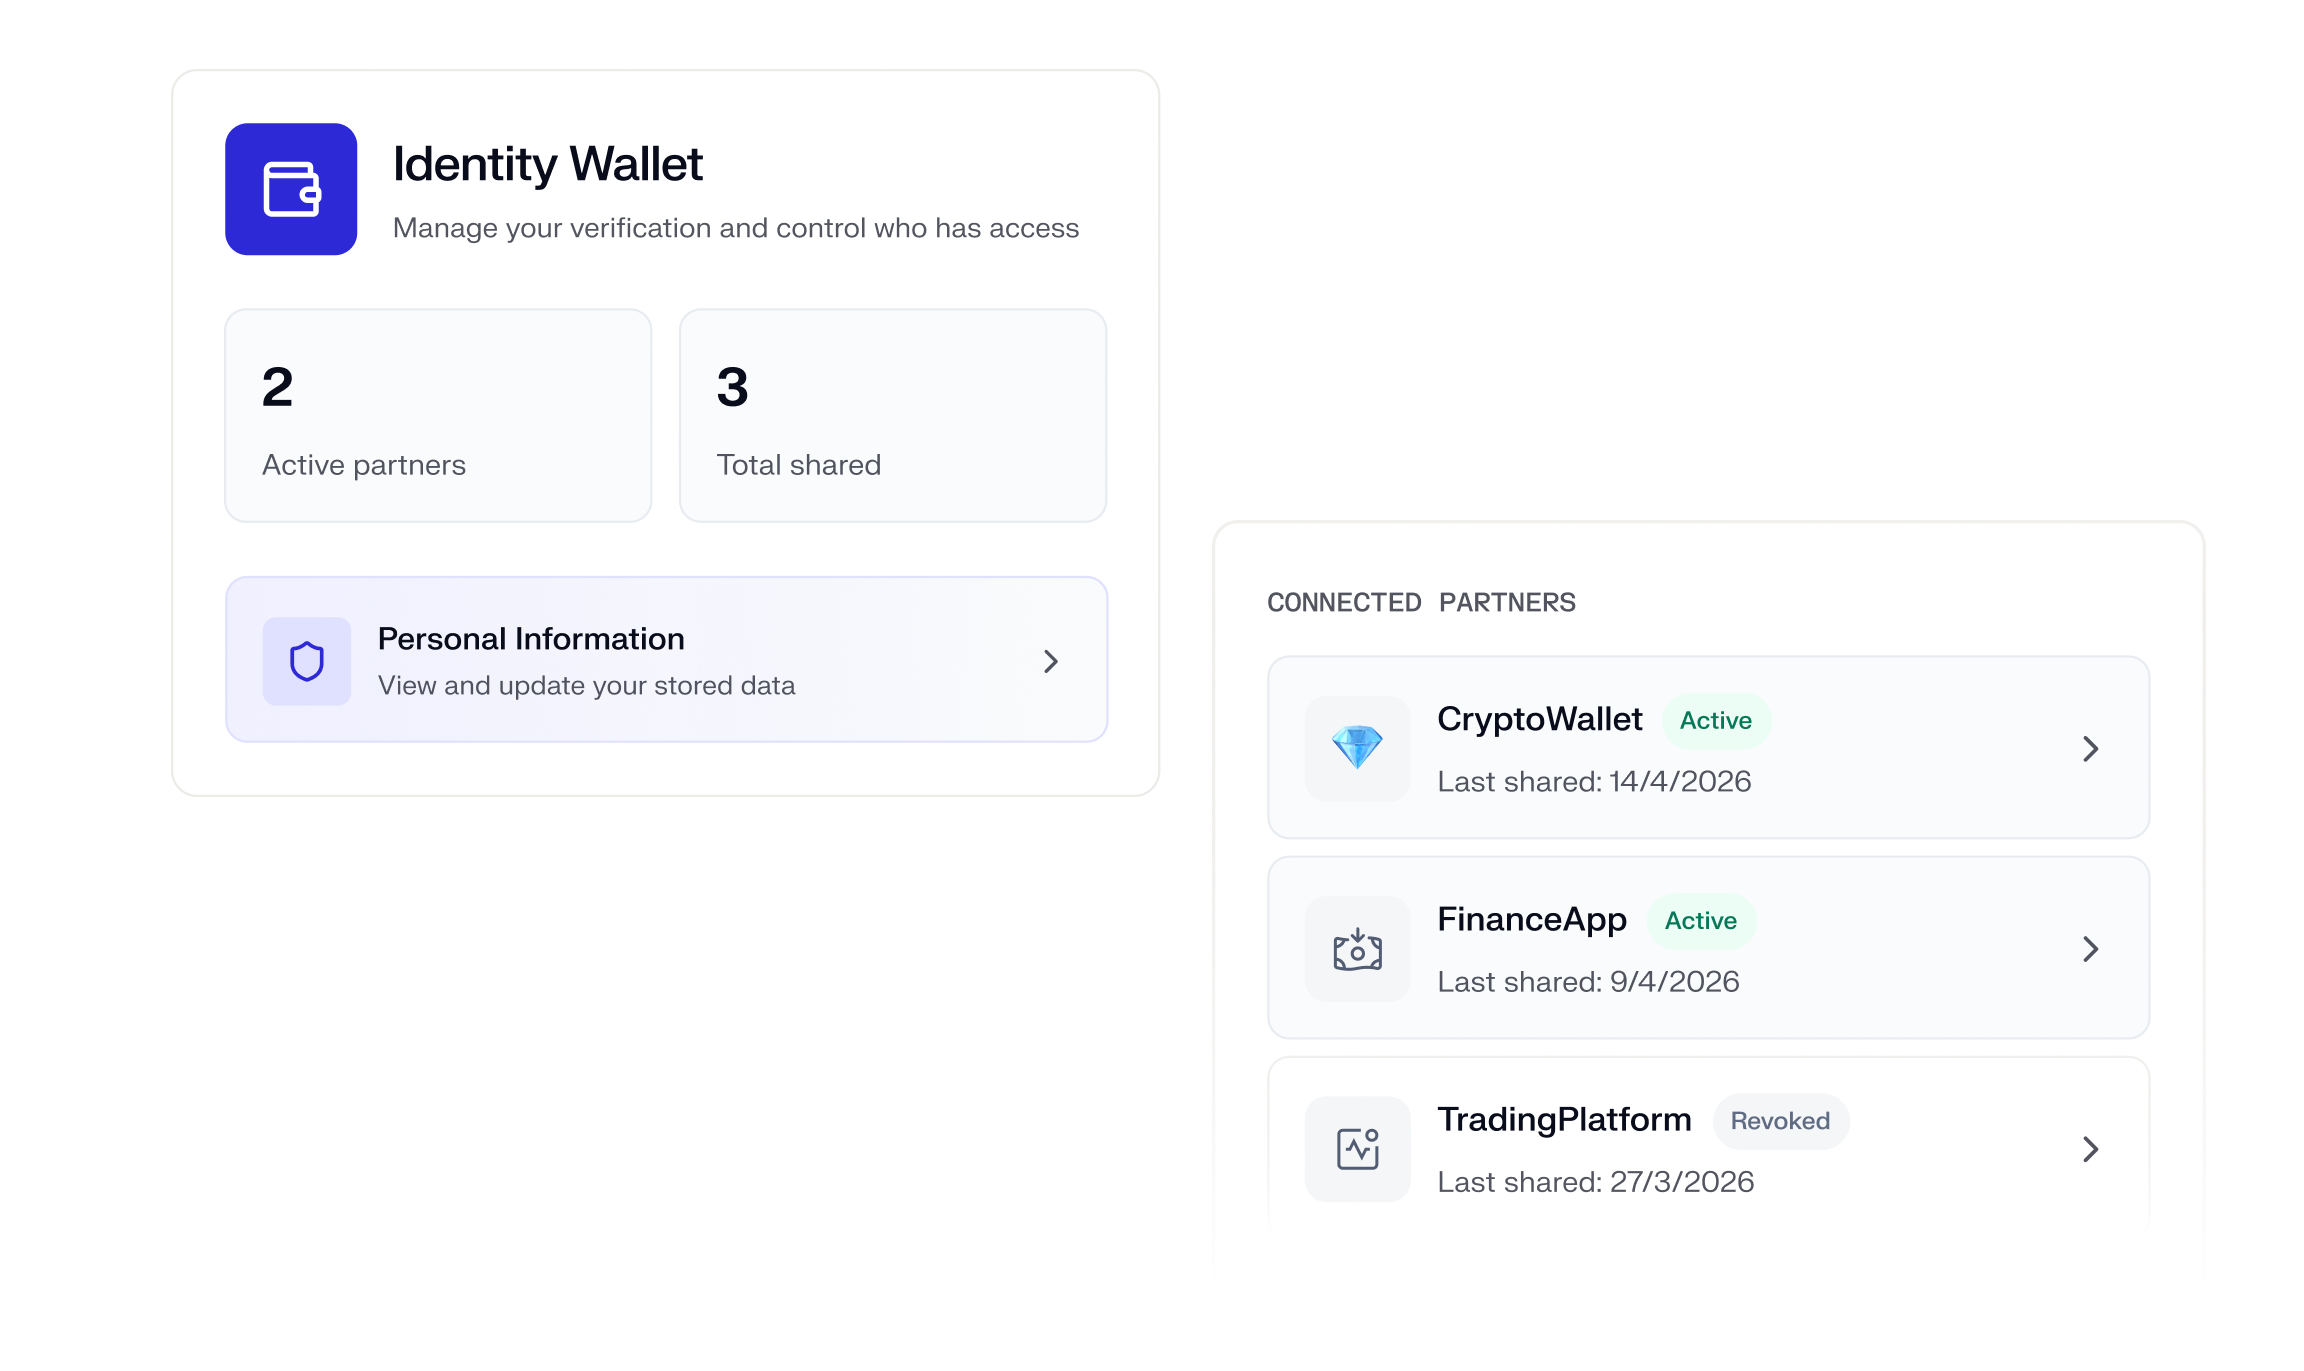

Move customers between approved services without unnecessary identity checks.

Make it easier for existing customers to access additional products and services.

Avoid paying for checks already completed when verification results meet your requirements.
Program Oversight
Orchestrate verification with full visibility and control
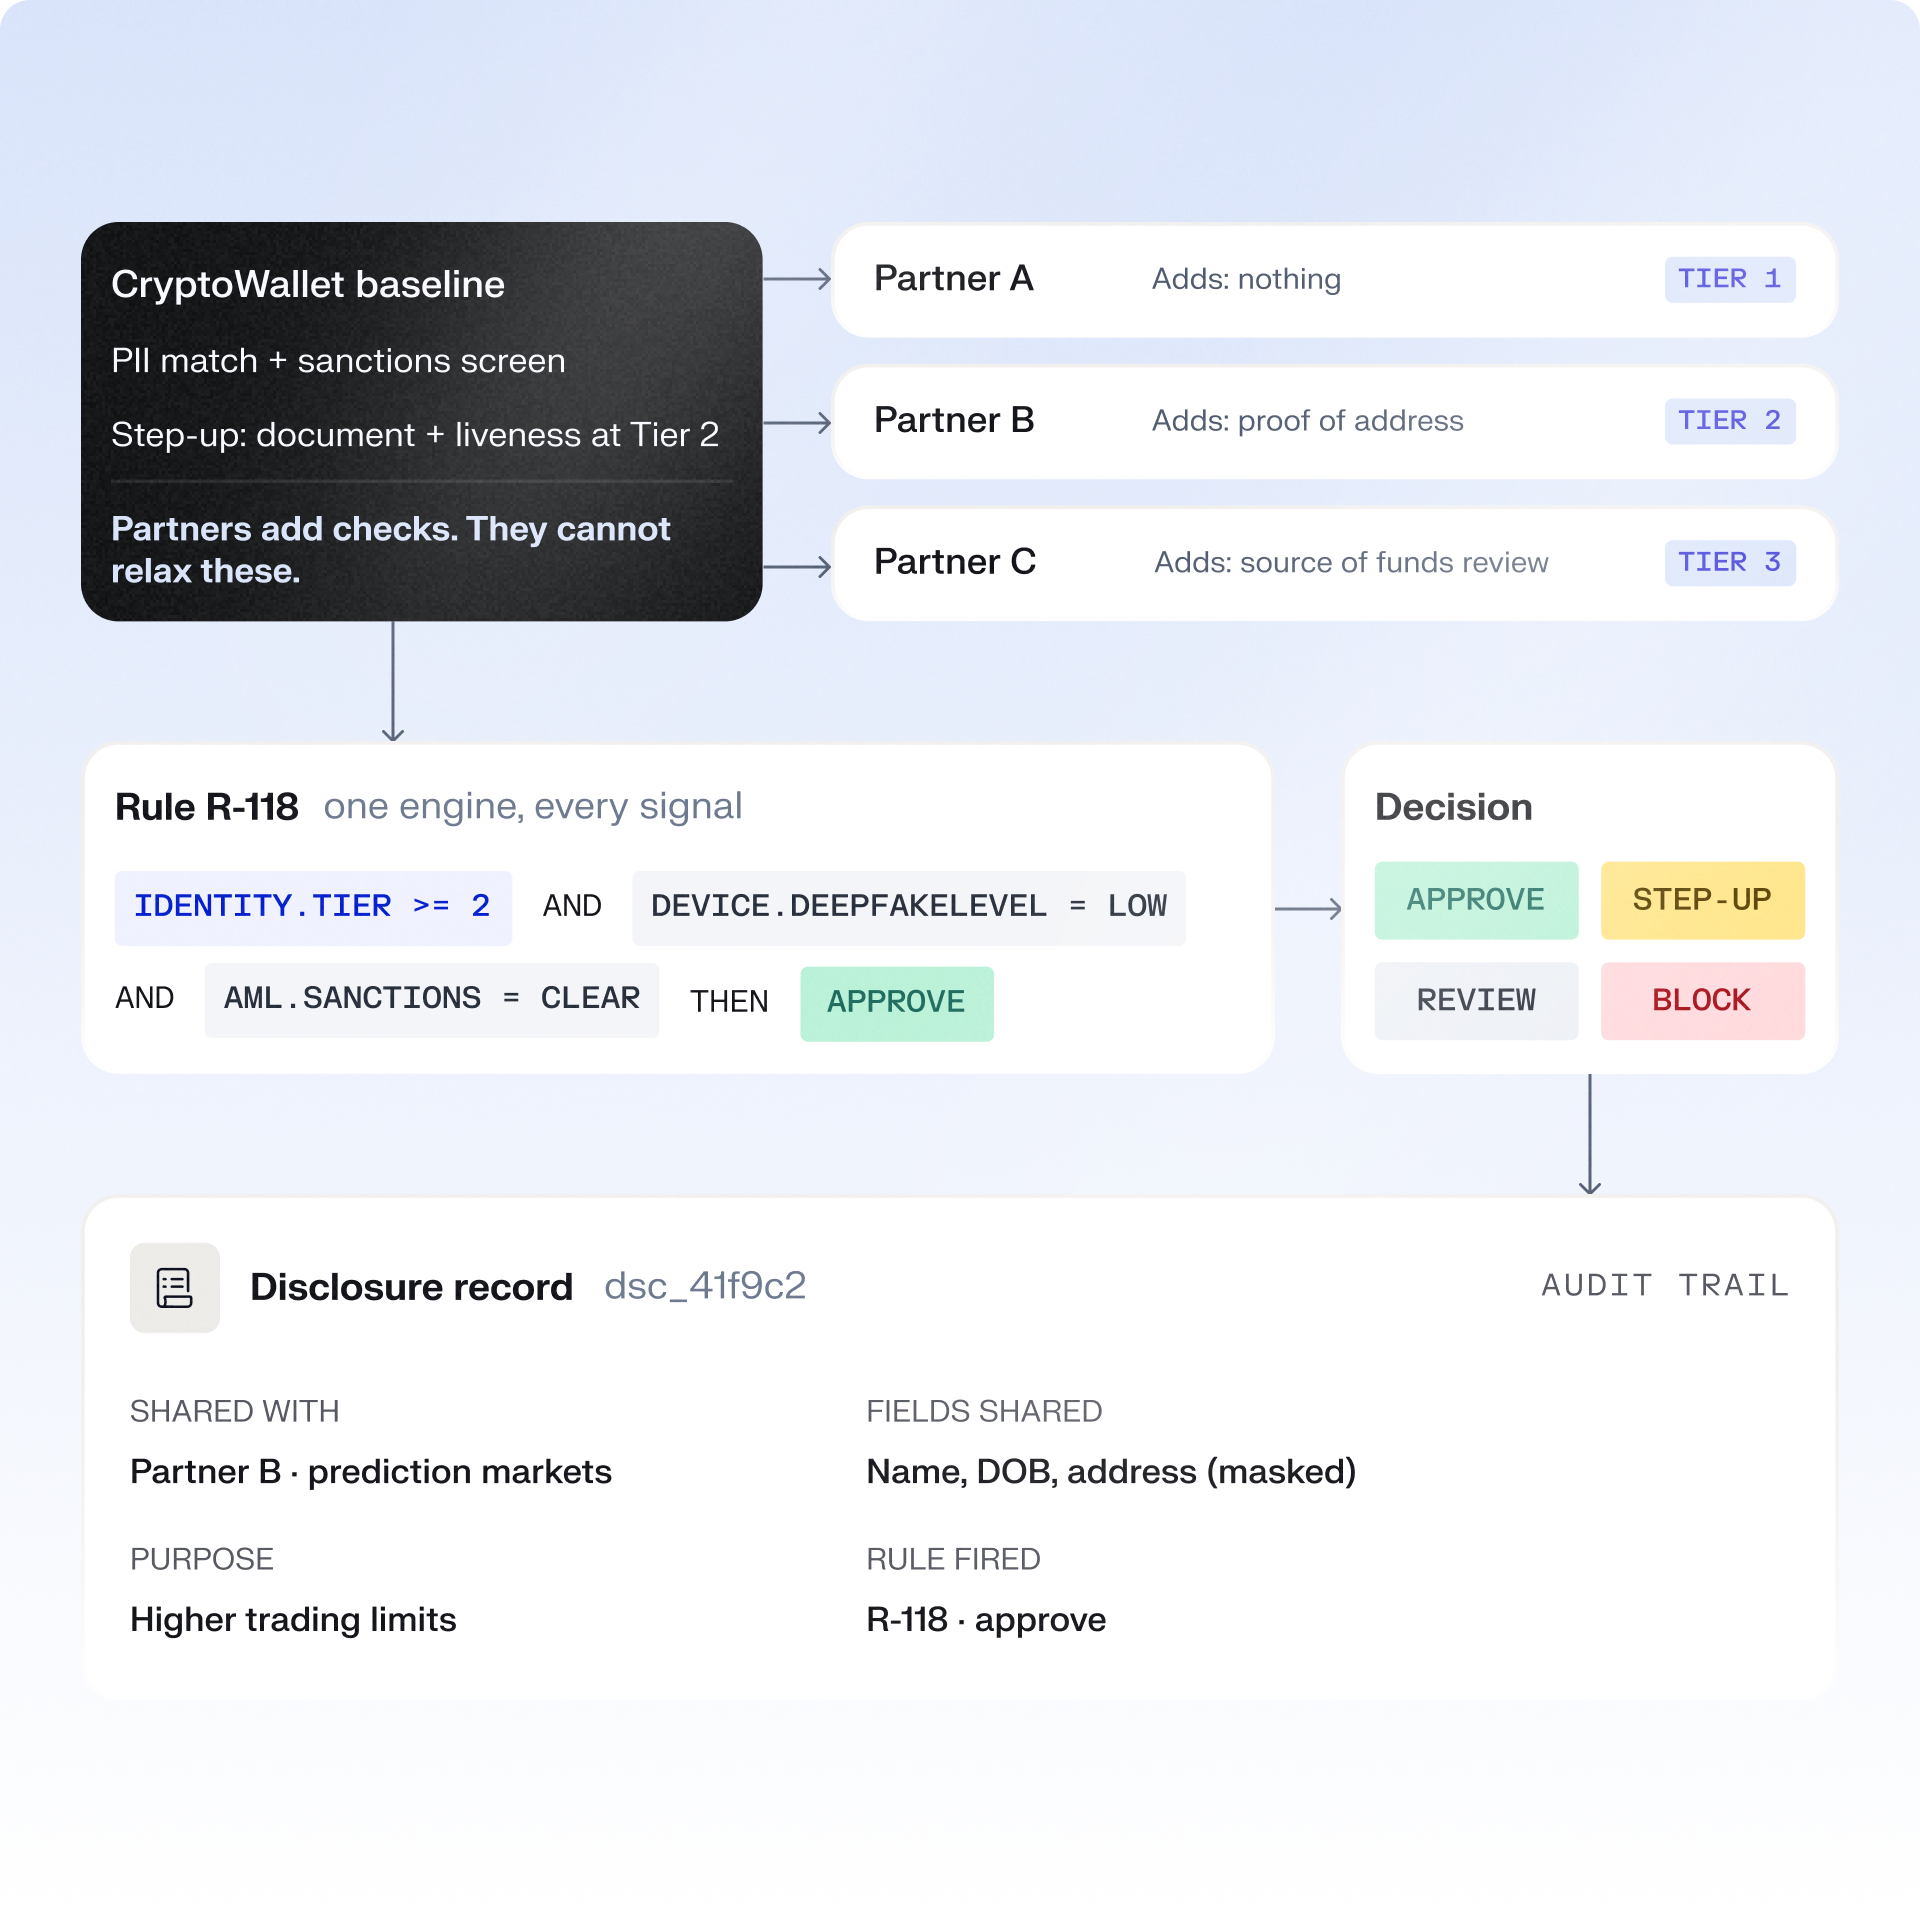
Manage identity sharing across partner programs, maintain control over verification requirements, and connect identity outcomes to fraud and AML decisions.
Product Expansion
Expand into new products without repeating KYC
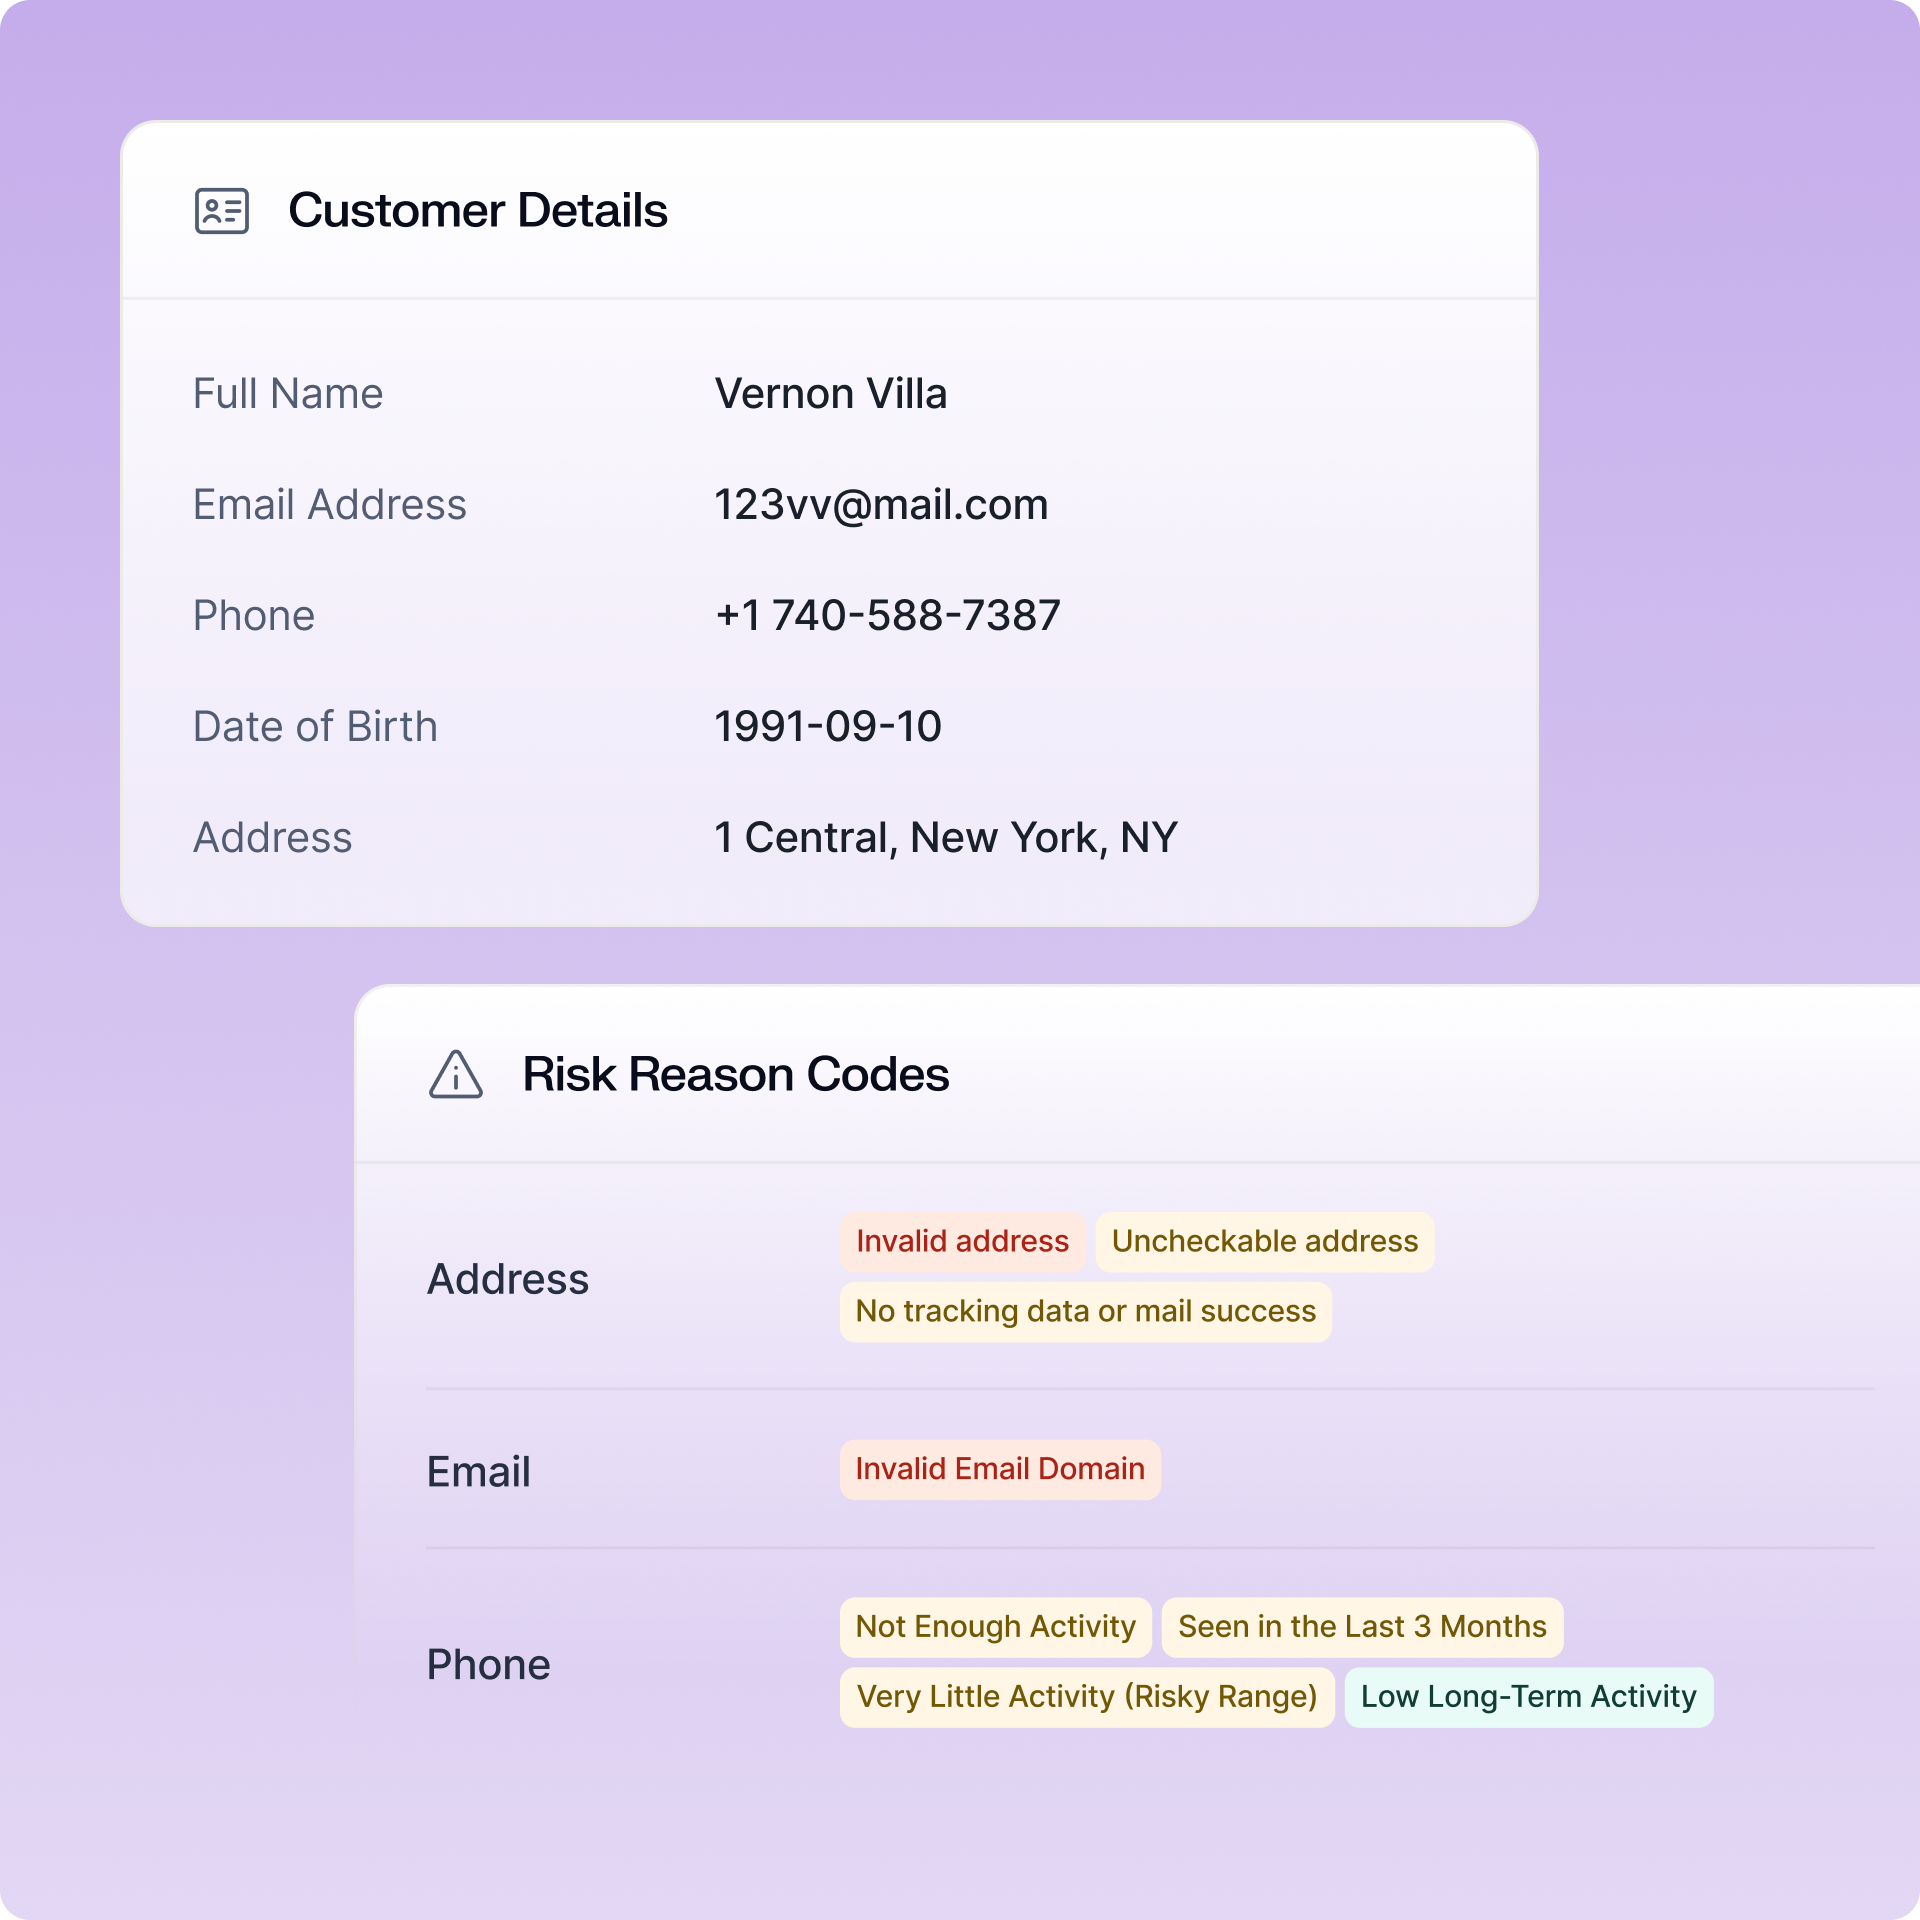
Introduce cards, lending, payments, crypto, and other financial services to your existing customer base while accounting for the different risk requirements of each offering.
Get up and running with reusable KYC
Bring Reusable KYC into your existing operations with minimal setup and full control over how verification works.
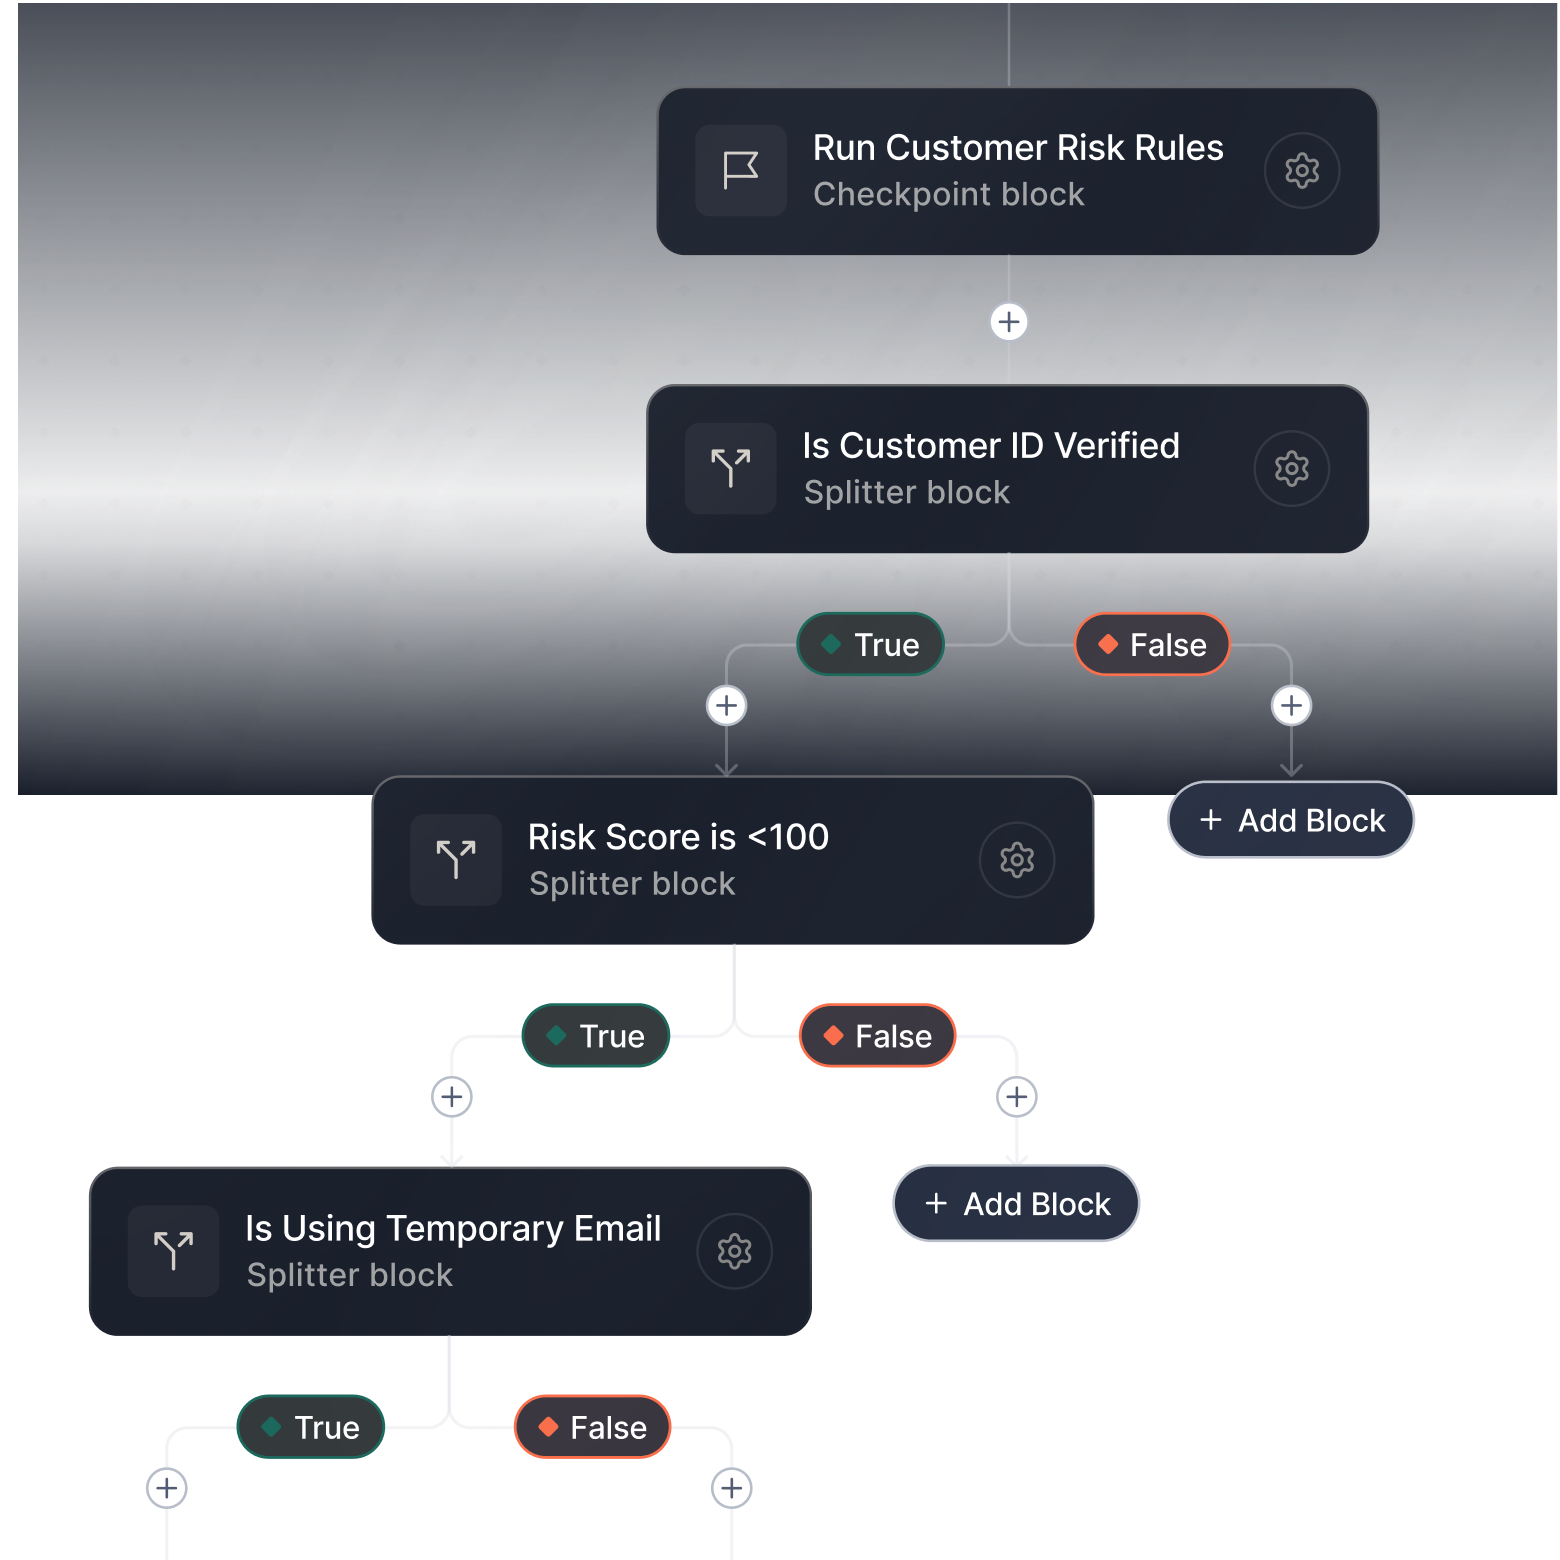
Define your KYC requirements and onboarding workflows
Set baseline KYC standards, tailor partner workflows, and define when additional checks are needed.
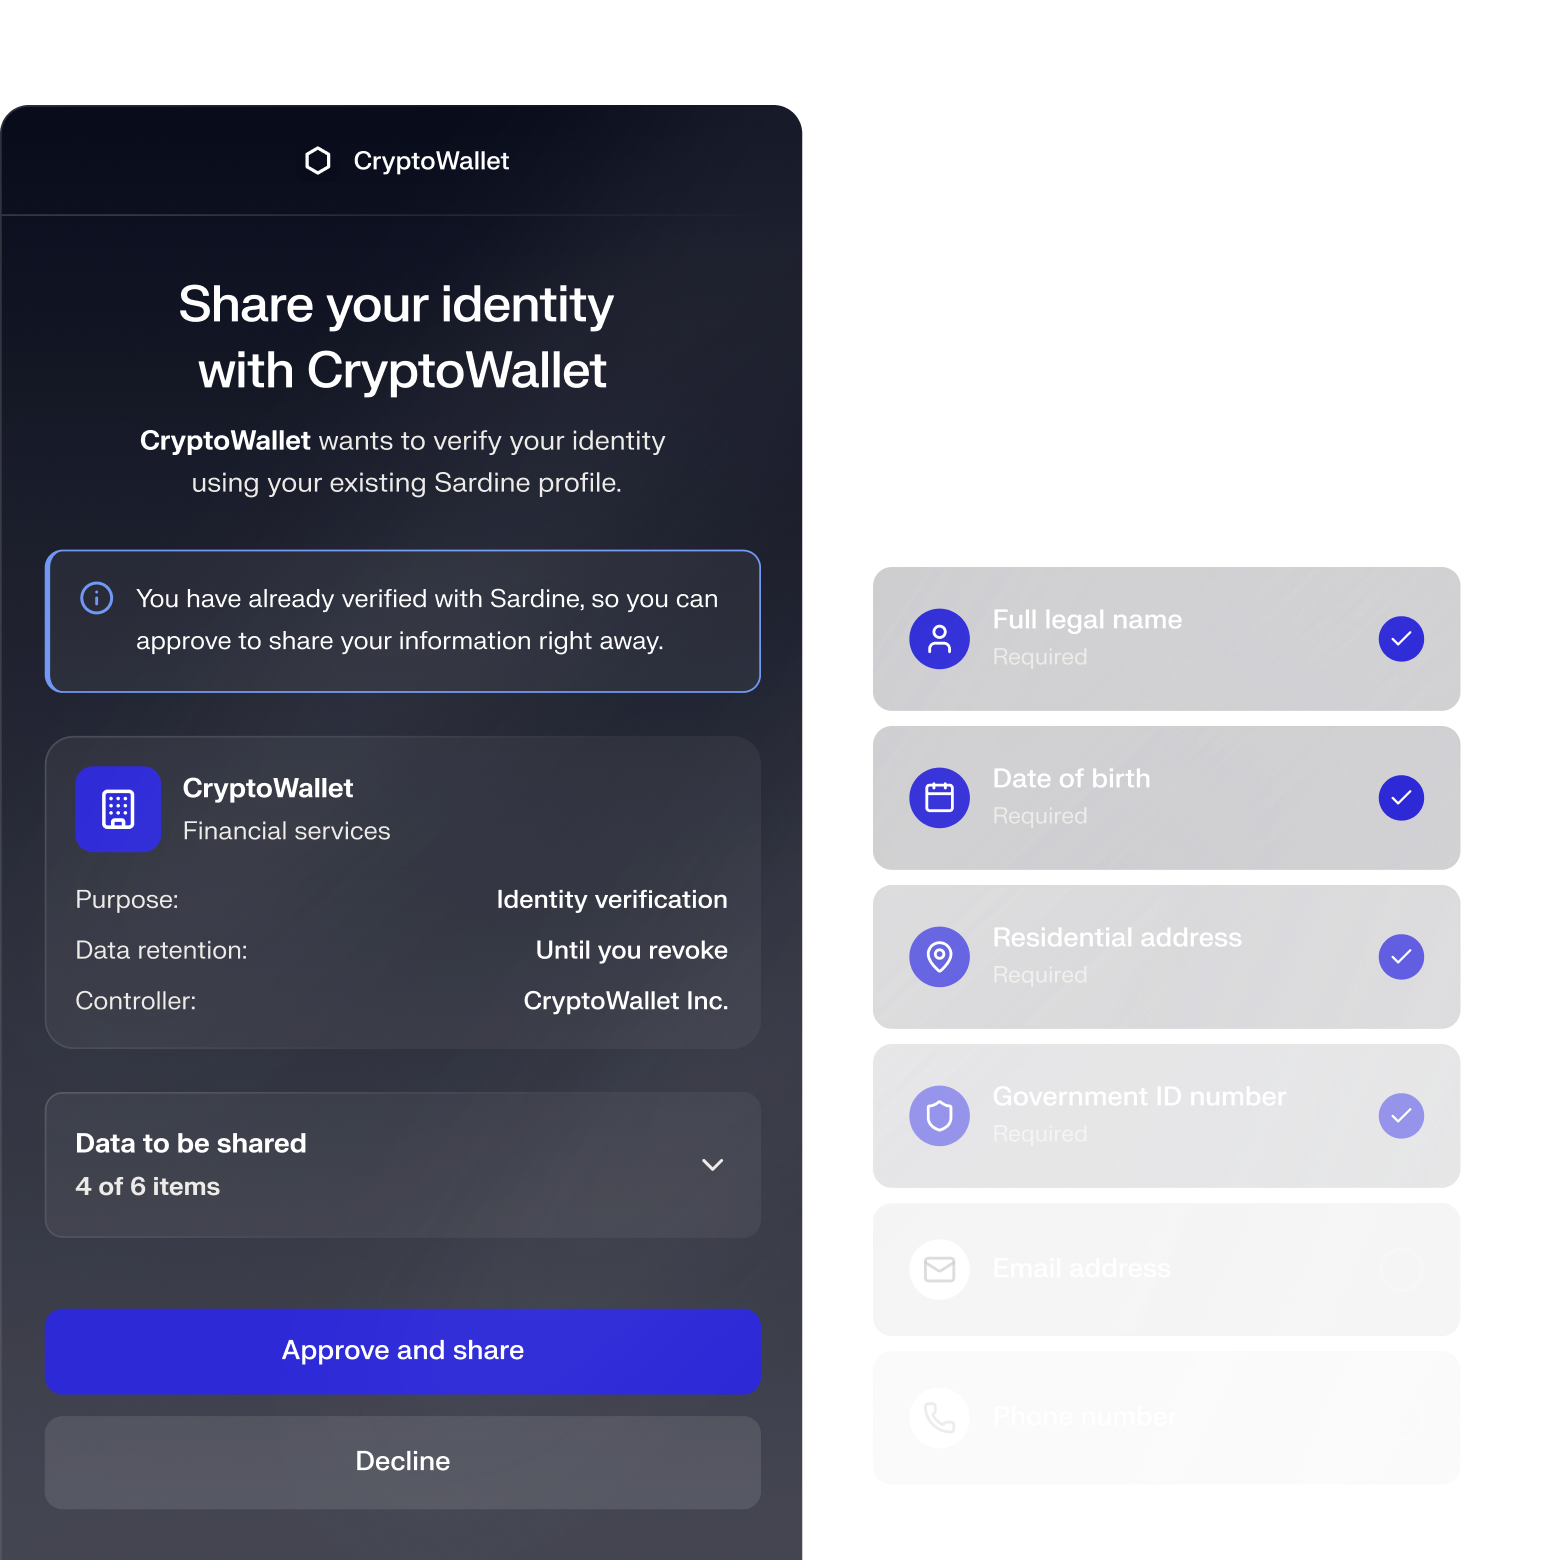
Capture consent with live fraud intelligence
Live device intelligence and behavioral signals help detect fraud and impersonation risks to confirm the right person is giving consent.
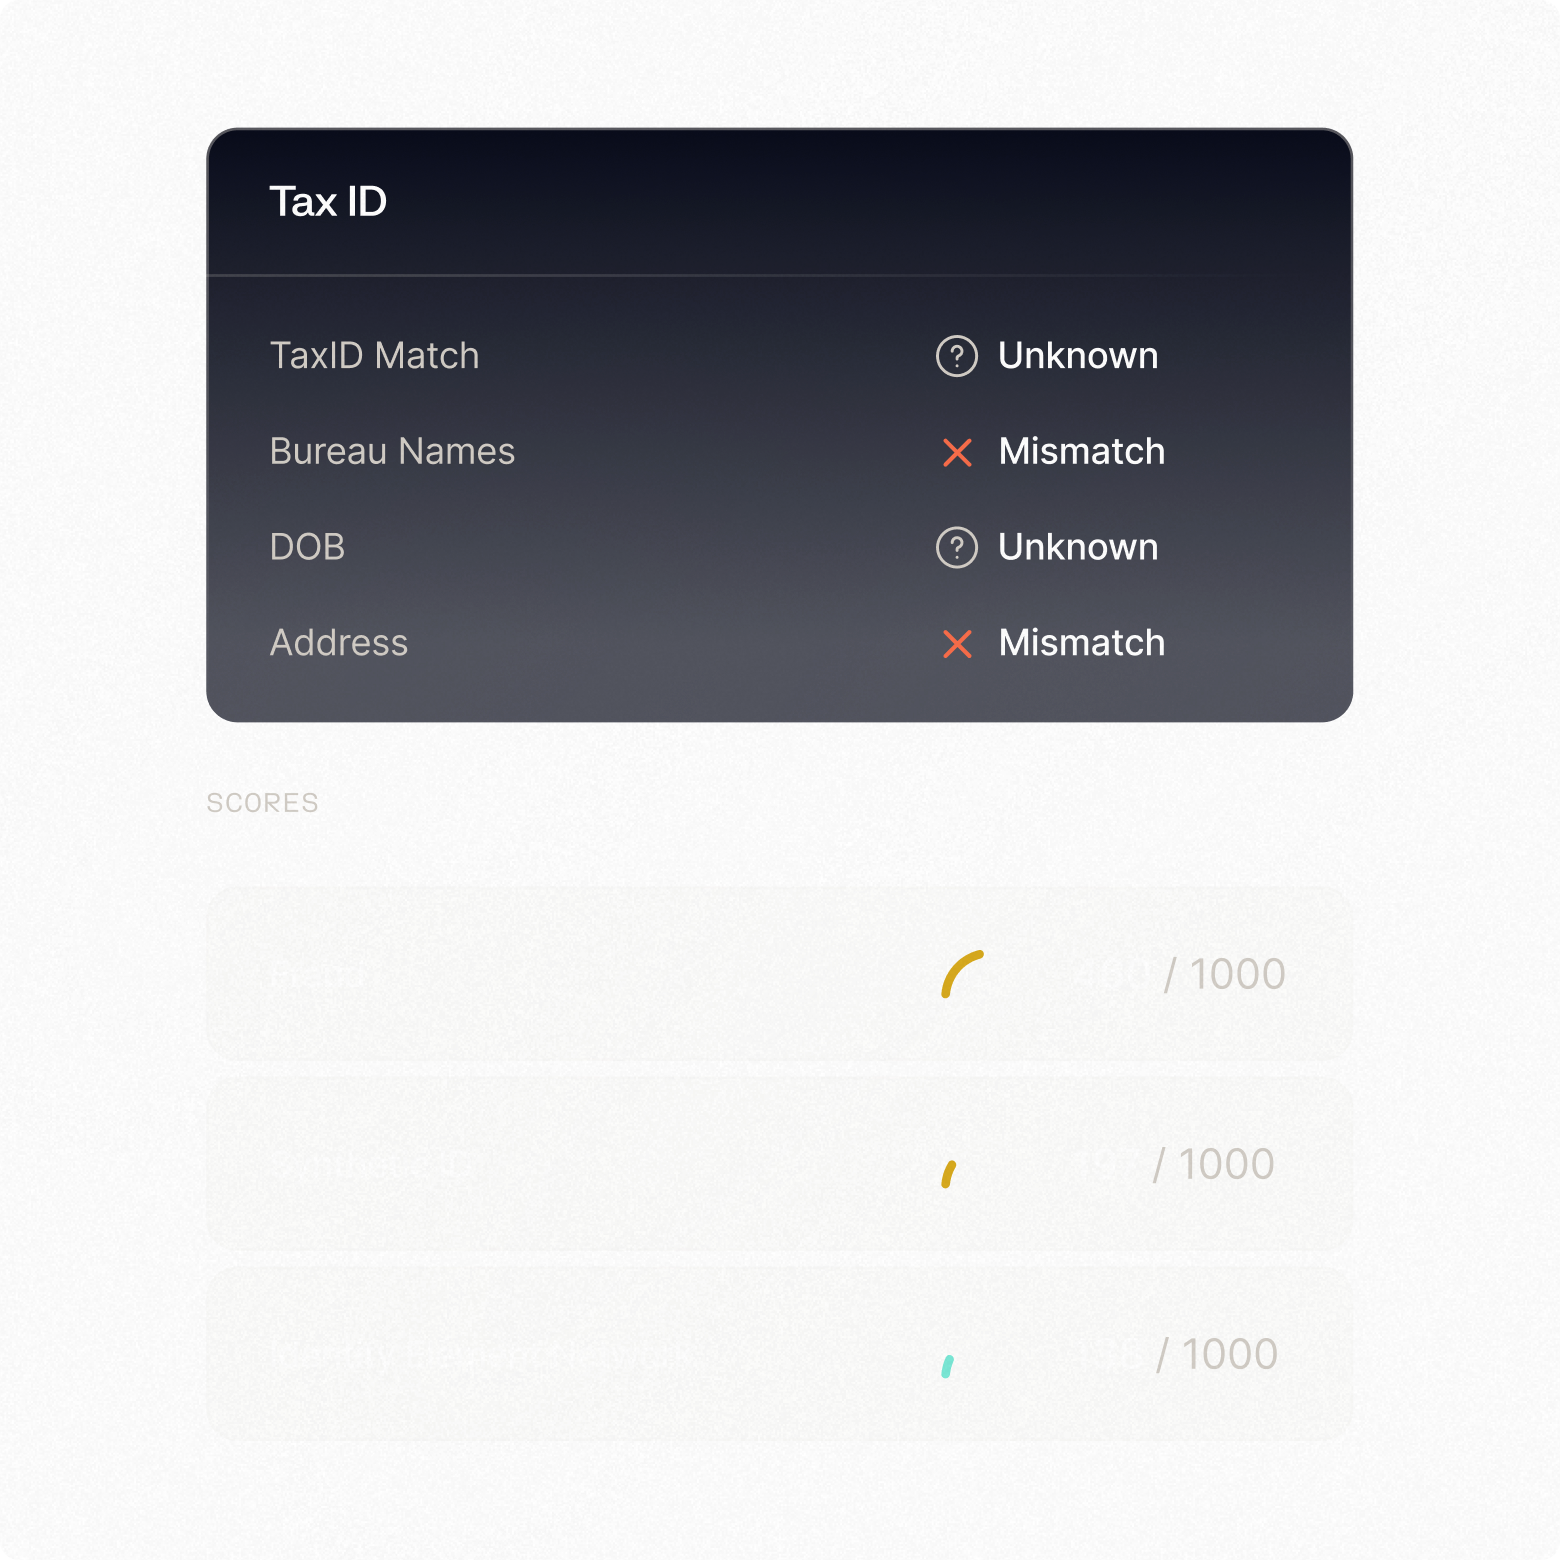
Validate KYC data against your requirements
Sardine’s rules engine checks shared identity data against your verification requirements, so you receive only the information you need.
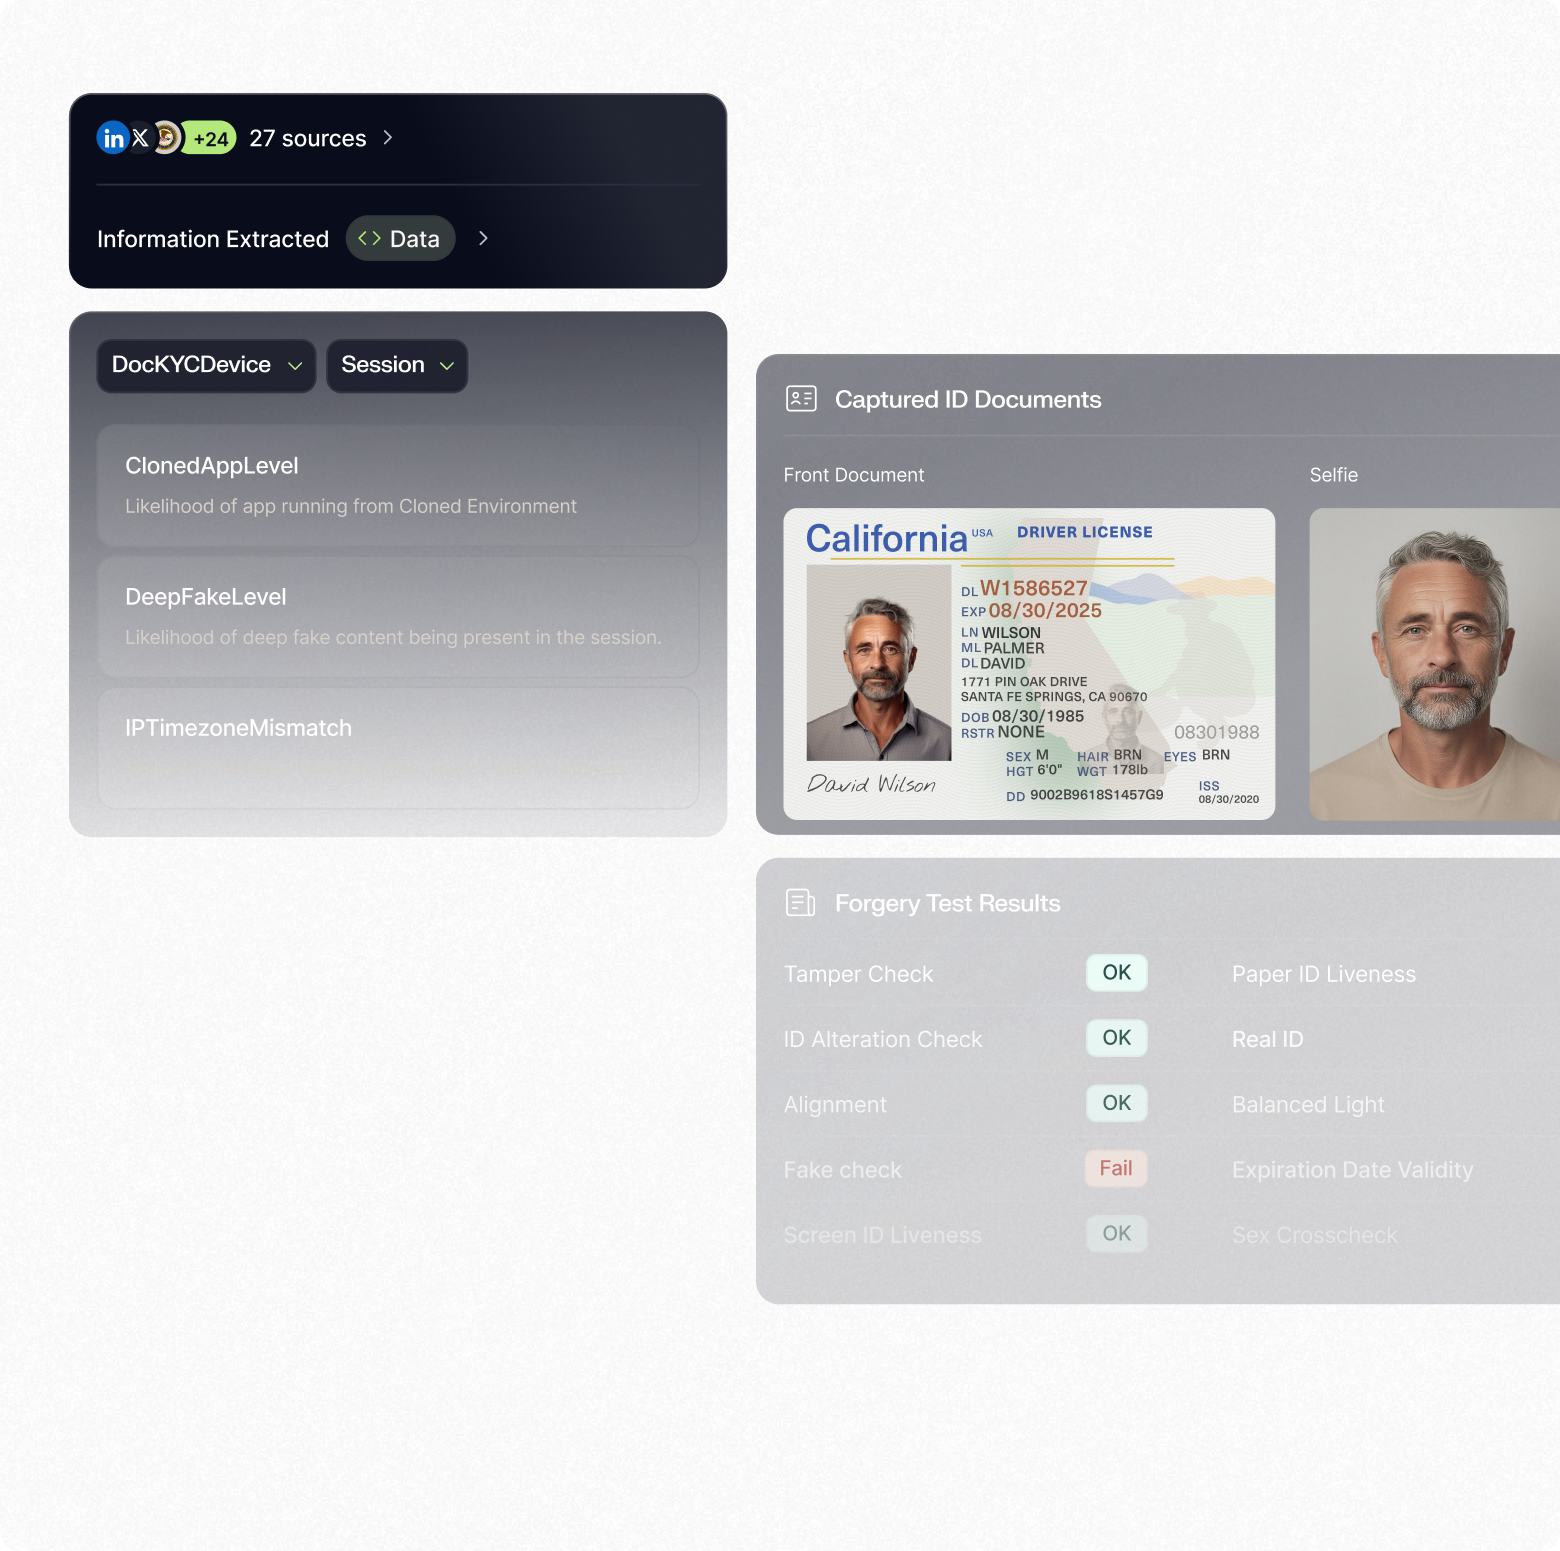
Step up when needed
Automatically fill verification gaps with targeted checks, such as selfies, liveness, or OTP, without restarting KYC.
Backed by the industry’s leading data platform
Data consortium
Prior verification is only as good as what you know now
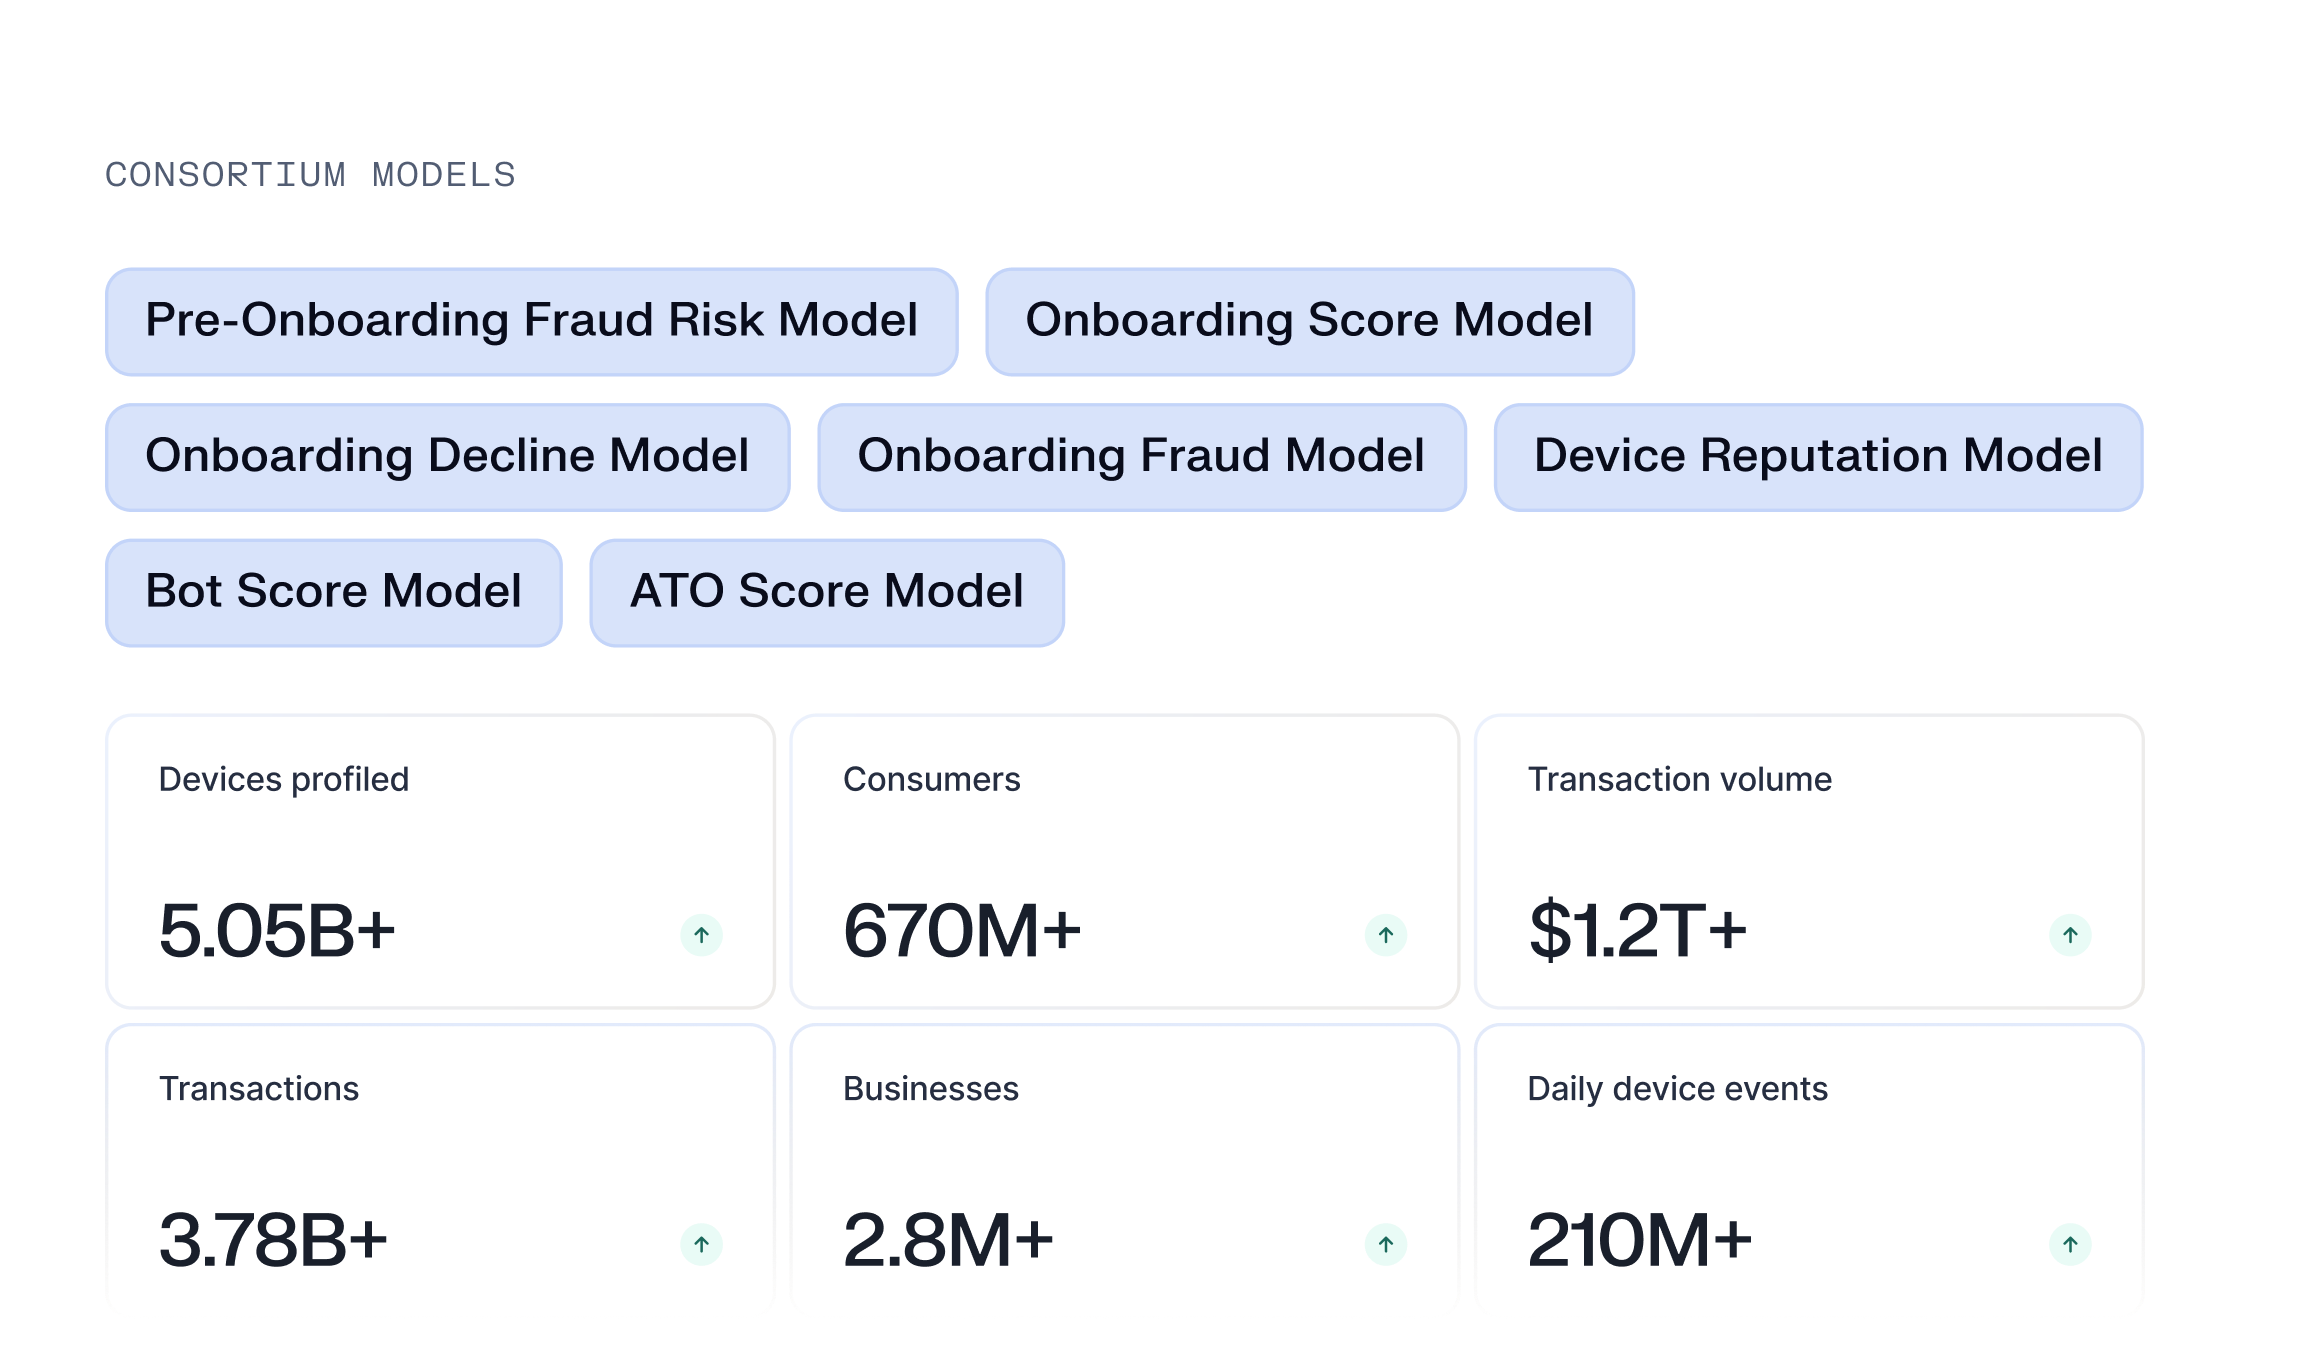
When a verified user returns, Sardine evaluates current device, behavioral, and consortium signals to uncover new fraud risks before reusing their identity.


Data Consortium
Benefit from cross-client insights
Use fraud outcomes, device associations, and behavioral patterns from Sardine’s consortium to make better-informed identity reuse decisions.
Rules & Workflows
Control when and how KYC gets reused
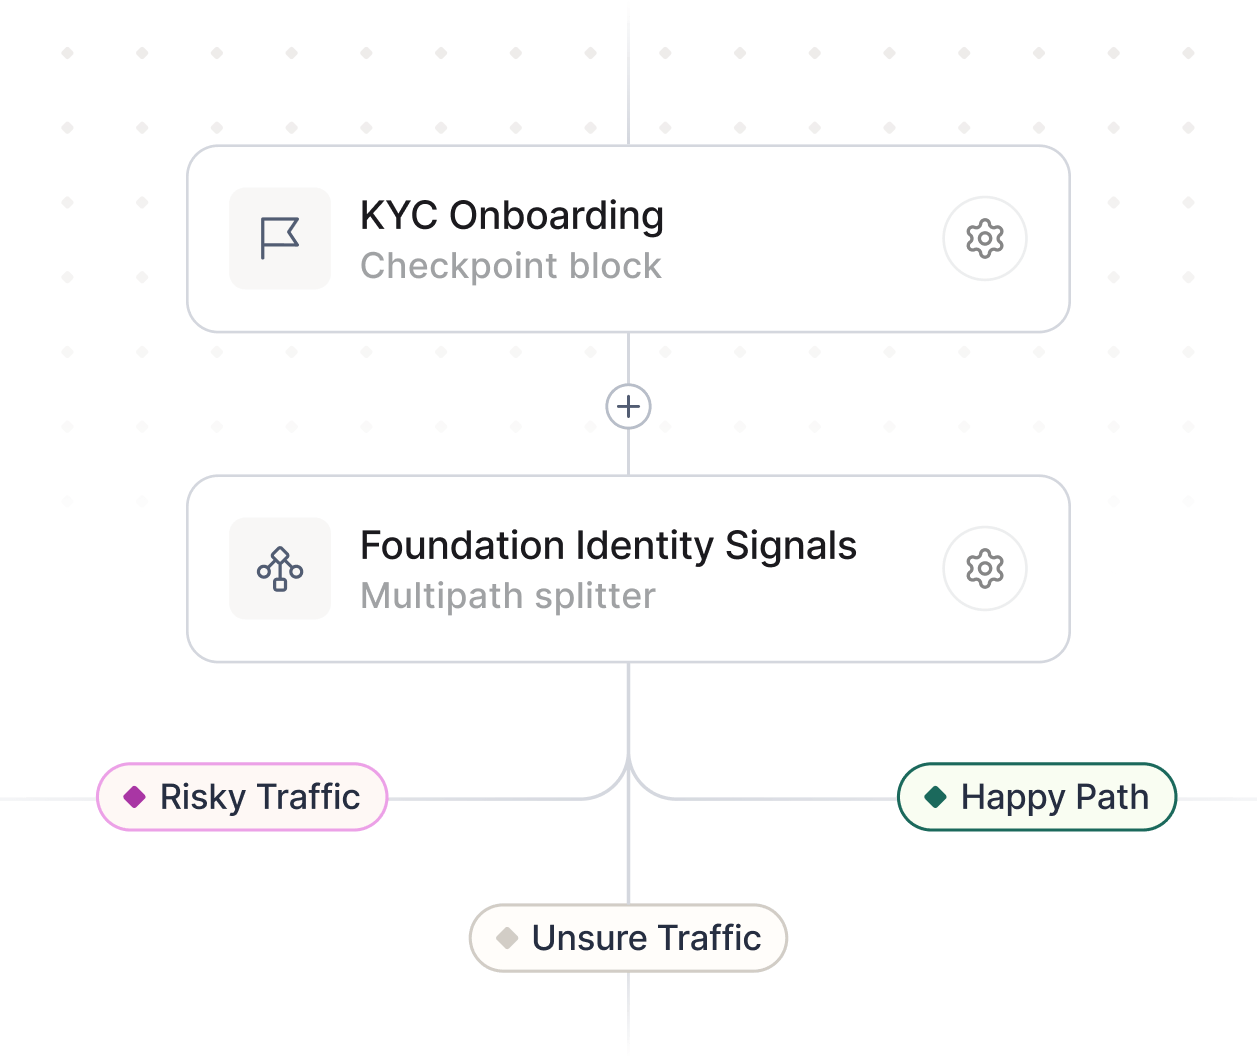
Set baseline verification requirements and configure partner-specific checks through Sardine’s rules engine, with policy control and auditability.
Machine Learning
Models that keep getting smarter
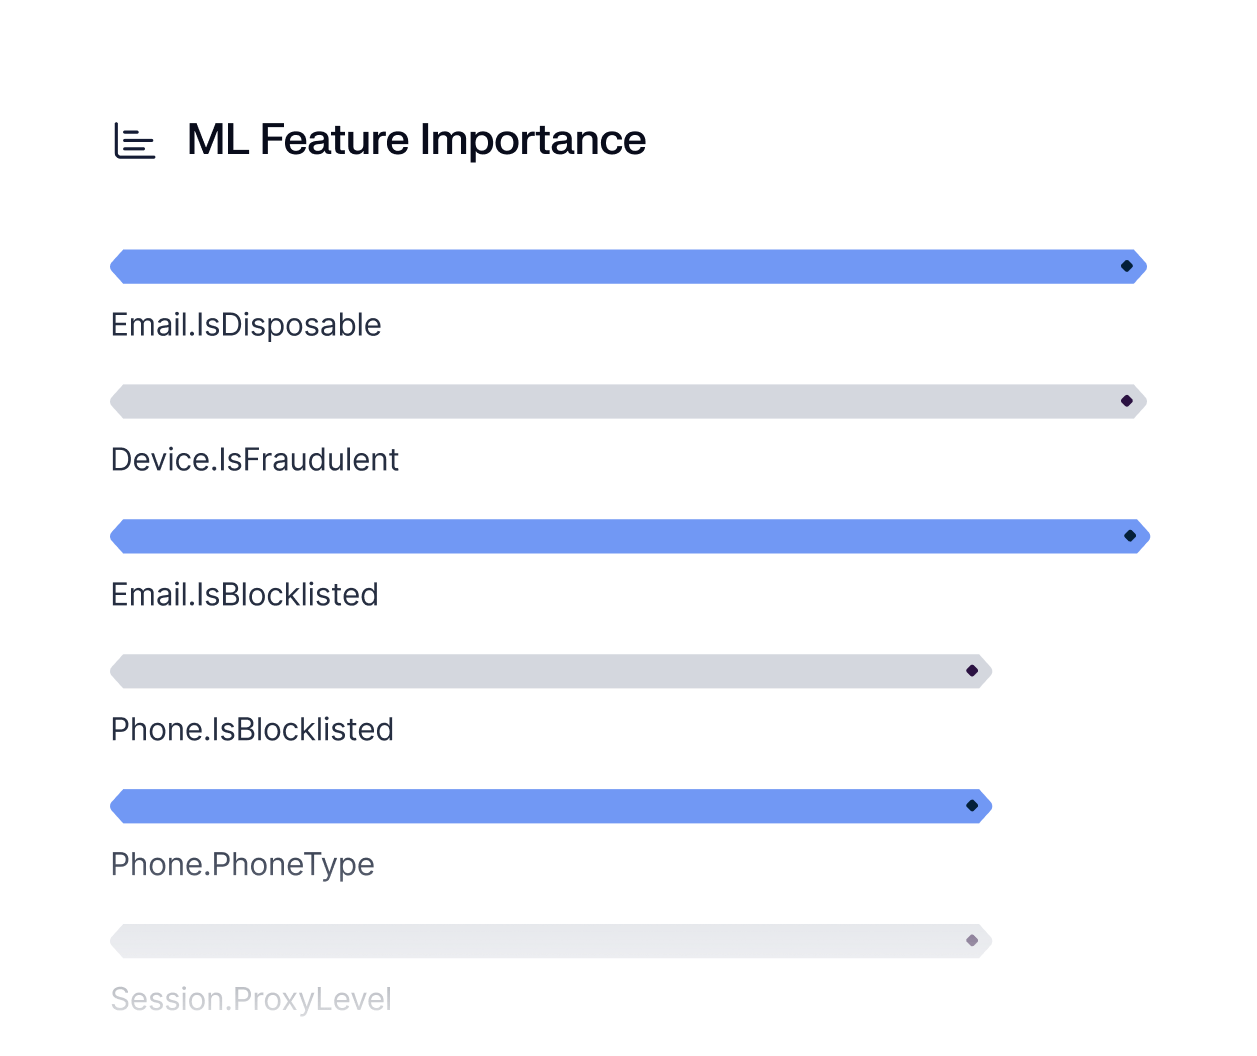
Continuously improve fraud detection with machine learning models informed by new signals and fraud outcomes across Sardine’s network.
Bring more customers onboard without starting KYC over
Frequently asked questions
How does Sardine decide whether a prior verification can be reused?
Reuse depends on the user’s consent for the partner and on whether the user’s current tier meets the partner’s requirements. If it does, the partner receives a decision and a tier. If it does not, Sardine triggers a step-up for the missing checks only.
What data does a partner receive?
A status token or a data payload, depending on the scope the partner is approved for. Each retrieval records who received what, when, and under which consent.
How does consent work when a user reaches a new partner?
A verified user reaches a new partner through a consent step. Sardine records the user’s consent for each partner, and a partner can retrieve a verified identity only subject to that consent.
How does Sardine fit into existing KYC and AML tooling?
Sardine runs identity, fraud, and AML screening through one configurable rules engine and returns a decision, a tier, and policy metadata to your app. Verification and consent run embedded or by redirect.
Does my app handle user PII?
For consumer platforms and wallets, no. Sardine holds the verification and your app receives a decision, a tier, and policy metadata. Regulated service providers receive a status token or a data payload, depending on approved scope.
Can we set different requirements for each partner?
Yes. Set tiers, required attributes, and step-up triggers for each partner or program. Reports export by customer or by partner.